Resources
HIPAA
What the Security Rule update actually asks of a smaller provider.
Everything we have published on the Security Rule, business associate agreements, and the rewrite that has been proposed but not finalized is collected here.
Everything on HIPAA
 HIPAAThe HIPAA Security Rule Hasn't Changed in 20 Years.The new HIPAA Security Rule is now expected July 2027, but the five major changes are coming. OrbitalFire and Kurt Bratten break down what healthcare orgs need to know now.
 HIPAAHIPAA Security Rule Update 2026: What Your Organization Should KnowThe first HIPAA Security Rule update in 20 years changes how covered entities verify vendor compliance — and what healthcare organizations need to do now.
 GovernanceCybersecurity Resilience: Why Compliance Isn’t EnoughPassing compliance checks doesn’t mean your business is secure. Learn why cybersecurity resilience determines whether your organization survives an incident.
 HealthcareHealthcare Cybersecurity and Resiliency Act of 2025What is the Healthcare Cybersecurity and Resiliency Act of 2025, and how does it relate to HIPAA? Learn what smaller healthcare providers should do now.
 Vulnerability ManagementWhy We Built Our Own Configuration BenchmarkThe CIS Benchmarks run to thousands of rules written for enterprises with a security team. The OrbitalFire Configuration Benchmark is the version a smaller business can actually hold to, mapped to HIPAA, NIST 800-171, NYSDFS, and SOC 2.
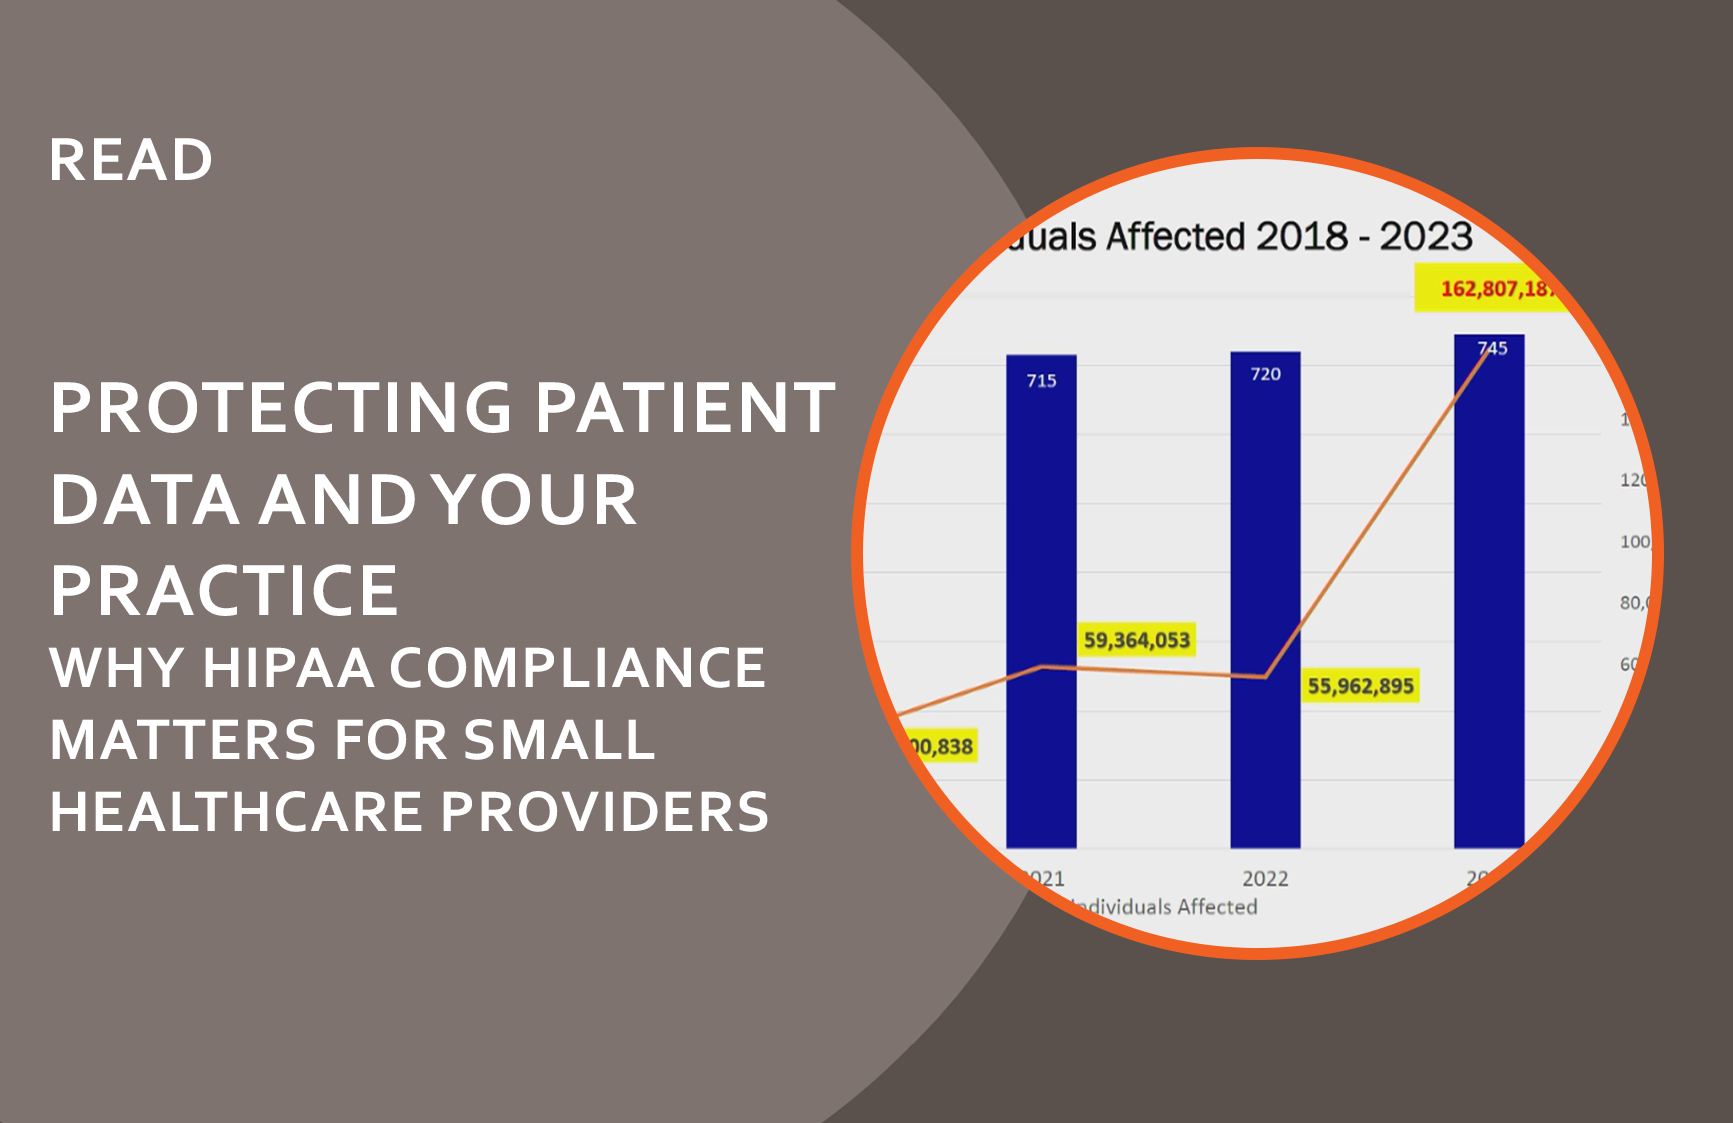 HIPAAProtecting Patient Data: Why HIPAA Compliance MattersFor small healthcare providers, maintaining HIPAA compliance is no small task. Recent data shows the risks of falling behind are greater than ever. Learn More
Where do you actually stand?
Reading about this is one thing. The Cybersecurity Readiness Checklist scores your own business in about five minutes, with no account and nobody calling you afterwards (unless you want us to).
Get Your Readiness ScoreBrowse the Whole Library
Would you rather talk it through? Tell us about your business.